Notes from the team
Blog.
What the team building Arvion is working on, what broke, and what we learned.
Latest
Antonio Firmiano
CEO · · 12 min read
Java4Shell depends on the CPU under your JVM
Java4Shell, tracked as CVE-2026-114938, is a reported flaw in the code the JVM uses to decode Base64 fast on AVX-512 processors. What's confirmed so far, the four conditions a server needs, read-only checks, the flag that turns the fast path off today, and where the fixed builds stand.
Read the post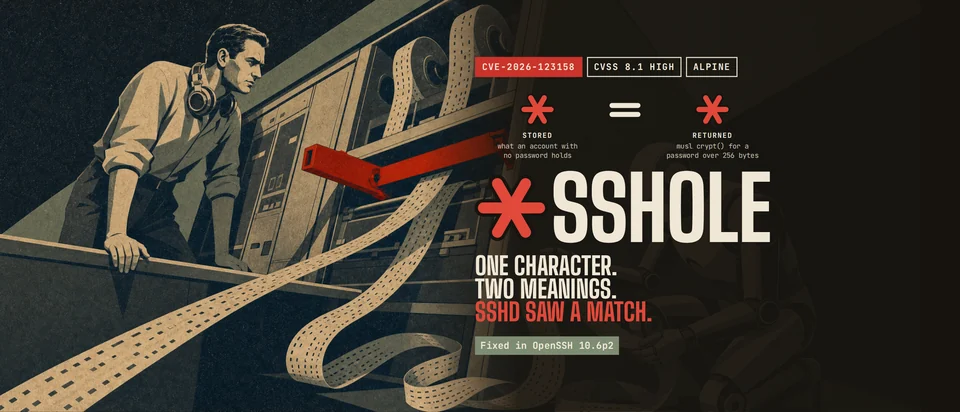
Antonio Firmiano
CEO · · 10 min read
The account had no password. Any long one worked.
CVE-2026-123158, called *sshole: on Alpine and other musl systems, sshd let anyone into accounts that have no password, with any password between 257 and 1,024 bytes. How three careful decisions from 2012, 2016 and 2022 lined up, which machines have the whole path, how to check yours, and the fix.
Read the post
Antonio Firmiano
CEO · · 7 min read
Not every finding is a way in. Trace the ones that are.
A security backlog is mostly findings an attacker can't reach. A review of the research on how few vulnerable dependencies are actually reached, how rarely CVEs are exploited, why noisy findings go unfixed, and why a finding gets fixed when it arrives with its fix.
Read the post
A product manager at Arvion
· 1 min read
What we shipped this week: stricter verdicts, more control over fix PRs
Release notes for the week of 26 October: exploitability verdicts backed by your code, a second review for actively exploited CVEs, no clean result for code we didn't analyze, and draft PRs, batch actions and test evidence for fixes.
Read the post
Antonio Firmiano
CEO · · 5 min read
After the PR: what a security fix has to survive
A security fix has four states: proposed, merged, deployed and holding. Most tooling stops at the first. What fails after the merge, why a 'not exploitable' statement is only true for one commit, and the ladder we're building to watch a fix in production.
Read the post
Antonio Firmiano
CEO · · 6 min read
Node2Shell isn't only in Node: how to find every copy of Brotli
CVE-2026-111497 is a bug in Google's Brotli decoder, and Node.js is one of many programs that carry their own copy. Where the other copies are, a one-line check that tells a fixed build from an old one, and which popular packages still ship the old decoder.
Read the post
Antonio Firmiano
CEO · · 5 min read
PHP2Shell in Docker: updating WordPress won't fix it
PHP2Shell is a pair of flaws in PHP itself. When WordPress runs in Docker, PHP comes from the image, so the fix comes from the image tag. How to see your PHP version and what to change for each kind of tag.
Read the post
Antonio Firmiano
CEO · · 4 min read
How to update PHP in a WordPress Docker container: pull, retag or rebuild
In Docker, PHP comes from the WordPress image, so the dashboard can't update it. How to read your image tag, pick a PHP branch, switch, check the result and roll back.
Read the post
Antonio Firmiano
CEO · · 3 min read
What PHP version is my WordPress site running? Six ways to check
Six ways to see the PHP version behind a WordPress site, from the dashboard to the command line, which one to trust, and how to read the number.
Read the post
Oleg Karapishchenko
Founding Engineer · · 7 min read
We let a local model fix our bugs. Then we had to check our checks.
In an internal side project, a 24B open-weight model on a MacBook fixed small bugs from our tracker. Most of my time went into fixing the checks that judged its work.
Read the post
A product manager at Arvion
· 3 min read
Fear Sells
Calls to slow down AI make headlines, but the real risk is the old security problems that never went away. Agents can help fix them, with people in control.
Read the post